CMMC vs. GSA’s New Cybersecurity Framework: What Contractors Should Know Written by: Marissa Pederson | Sr. Director of Program Management Government Contracting Cybersecurity CMMC NIST Compliance Learn More about CMMC vs. GSA’s New Cybersecurity Framework: What Contractors Should Know
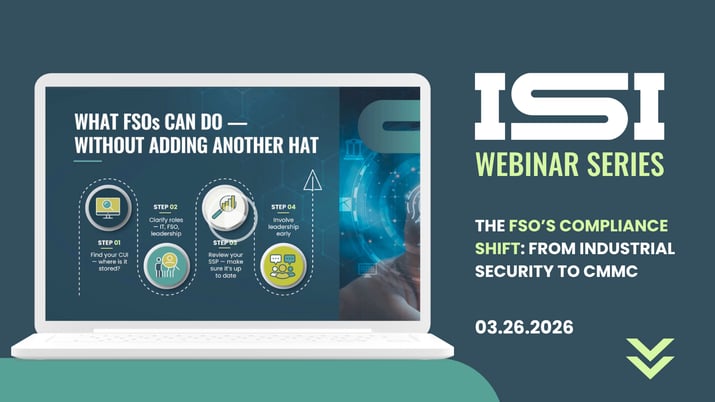
THE FSO'S COMPLIANCE SHIFT: FROM INDUSTRIAL SECURITY TO CMMC | WEBINAR Written by: ISI Webinar Learn More about THE FSO'S COMPLIANCE SHIFT: FROM INDUSTRIAL SECURITY TO CMMC | WEBINAR
What Should Be in Your System Security Plan (SSP) for CMMC Level 2? Written by: John Nolan | Vice President of Compliance Government Contracting Cybersecurity CMMC NIST Compliance Learn More about What Should Be in Your System Security Plan (SSP) for CMMC Level 2?
CMMC Is Not a Cyber Problem. It’s a Business Risk Issue Written by: Bryan Champagne | President, IT & MSP Services Government Contracting Cybersecurity CMMC Learn More about CMMC Is Not a Cyber Problem. It’s a Business Risk Issue
The Three-Year Myth: The Real CMMC Timeline for the Defense Industrial Base | Webinar Written by: ISI Webinar Learn More about The Three-Year Myth: The Real CMMC Timeline for the Defense Industrial Base | Webinar
CMMC POA&Ms Explained: What You Can and Cannot Defer Written by: John Nolan | Vice President of Compliance Government Contracting Cybersecurity CMMC NIST Compliance Learn More about CMMC POA&Ms Explained: What You Can and Cannot Defer
Do You Really Need a GRC Platform for CMMC? Written by: John Nolan | Vice President of Compliance Government Contracting CMMC Learn More about Do You Really Need a GRC Platform for CMMC?
Security Advisory: Stryker Cyber Incident Sparks Elevated Phishing Risk Written by: Muhammad Ali | Vice President, Cybersecurity Operations Advisories Learn More about Security Advisory: Stryker Cyber Incident Sparks Elevated Phishing Risk
Security Advisory: Heightened Cyber Risk Related to Iran Conflict + Cloud Service Disruption Planning Written by: Muhammad Ali | Vice President, Cybersecurity Operations corporate espionage spotting spies Cybersecurity espionage Advisories Learn More about Security Advisory: Heightened Cyber Risk Related to Iran Conflict + Cloud Service Disruption Planning