What Does “Good Enough” Look Like in CMMC?
Written by: John Nolan | Vice President of Compliance
Learn More about What Does “Good Enough” Look Like in CMMC?
Written by: John Nolan | Vice President of Compliance
Learn More about What Does “Good Enough” Look Like in CMMC?
Written by: John Nolan | Vice President of Compliance
Learn More about 32 CFR is final. what's next?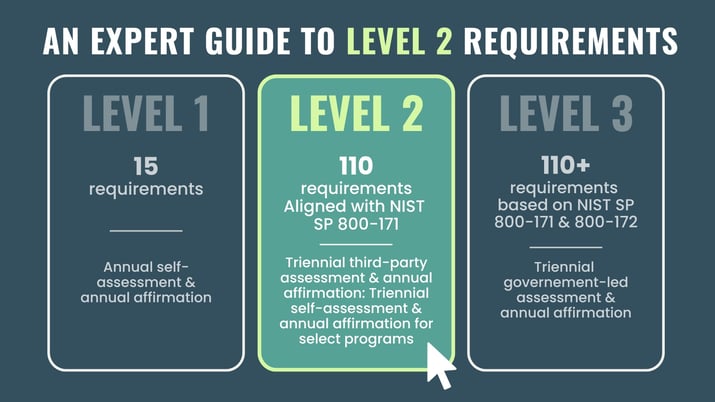
Written by: John Nolan | Vice President of Compliance
Cybersecurity CMMC Guide NIST Compliance
Learn More about CMMC LEVEL 2: AN EXPERT GUIDE TO LEVEL 2 REQUIREMENTS
Written by: John Nolan | Vice President of Compliance
CMMC Managed IT Guide NIST Compliance
Learn More about How to Pass Your NIST 800-171 Assessment and the Most Commonly Failed Objectives
Written by: John Nolan | Vice President of Compliance
Cybersecurity CMMC Managed IT Guide NIST Compliance
Learn More about Your Guide to CMMC Level 3 Compliance for Defense Contractors
Written by: John Nolan | Vice President of Compliance
Learn More about How to Choose a C3PAO
Written by: John Nolan | Vice President of Compliance
Cybersecurity CMMC Managed IT NIST Compliance SMB
Learn More about CMMC Level 2 Assessment: A First-Hand Perspective
Written by: John Nolan | Vice President of Compliance
CMMC Managed IT Guide NIST Compliance
Learn More about How to Develop a System Security Plan (SSP) for CMMC
Written by: John Nolan | Vice President of Compliance
Cybersecurity CMMC Guide NIST Compliance
Learn More about How to Write a POA&M